At this year’s OCP Global Summit, Microsoft announced Project Tessera, the evolution of the Azure Integrated Hardware Security Module (HSM), into a fully open-source initiative developed in collaboration with Marvell®, Oracle, and Open Compute Project (OCP). Project Tessera advances our broader commitment to open, industrywide standards for platform security.
The motivation behind Project Tessera is straightforward: the entire industry benefits when we collaborate and advance hardware security together.
Project Tessera carries forward the workload directly attached to the HSM architecture introduced by Azure Integrated HSM, making the architecture, specifications, protocols, drivers, software, firmware, and reproducible build environments open source for the broader community. Over time, the initiative will advance toward a fully open-source silicon implementation, while making hardware broadly available, enabling organizations across the ecosystem to adopt, integrate, and contribute to the platform.
This approach builds on the model Microsoft established with other industry collaborators on Caliptra, a fully open-source silicon root-of-trust that has since been broadly adopted across the hardware ecosystem. Through Project Tessera, industry leaders including Microsoft, Marvell®, Oracle, and the Open Compute Project will apply that same model of transparency and collaboration to advance hardware key protection with the industry.
The cybersecurity landscape is rapidly changing, and protecting keys and credentials has never been more important. We are now facing two generational transformations that are fundamentally reshaping how we view the cybersecurity landscape:
- AI is increasing the speed and scale of cyberattacks
AI-orchestrated attacks are increasing the scale, speed, and sophistication of attacks, giving adversaries new ways to operate and compressing the time between vulnerability discovery and exploitation. These capabilities amplify risks such as credential theft, key exfiltration, and signing abuse.
Keys and credentials are high-value control assets. When compromised, they can enable attackers to impersonate trusted entities, bypass security controls, authorize malicious operations, expose sensitive data, and undermine software security defenses. Protecting these assets requires infrastructure with layered, hardened protections capable of withstanding sustained attacks across multiple concurrent attack vectors.
- Quantum computing is changing the cryptographic risk horizon
Quantum computing promises transformative advances, but it also presents a risk to many of today’s cryptographic algorithms. A sufficiently powerful quantum computer could break widely used public-key cryptography, undermining digital signatures, authentication, and identity verification.
Post-quantum cryptography was once viewed as an important but distant technology shift. Advances in quantum computing have changed that perspective as organizations recognize the urgency, scale, and complexity of the transition. HSM-backed signing infrastructure will be among the first critical systems to migrate, requiring HSMs that support post-quantum cryptography and are interoperable with classical HSMs to support migration.
These emerging threats motivated the development of Azure Integrated HSM, which was designed to meet rigorous security standards for hardware-based key protection, while also accelerating Microsoft’s transition to post-quantum cryptography through scale deployments of quantum resilient integrated HSMs.
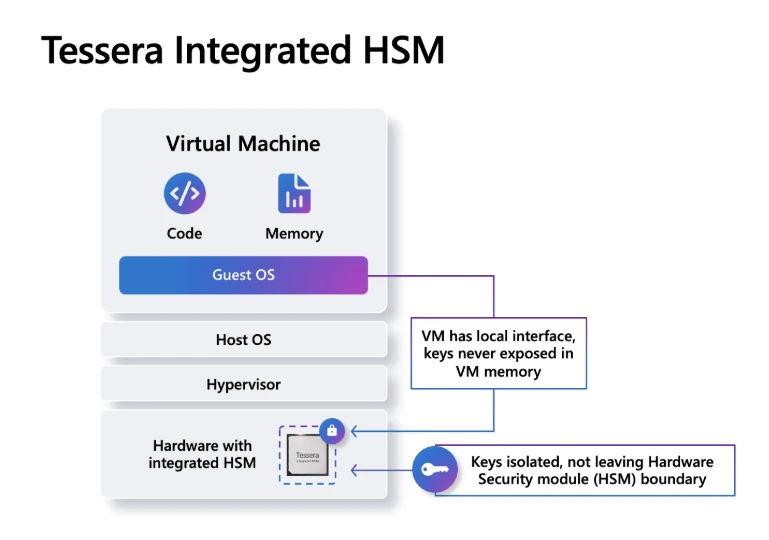
Azure Integrated HSM introduced a workload-attached HSM that performs cryptographic operations closer to the workload while keys remain continuously protected within the HSM security boundary. This architecture strengthens key protection, improves cryptographic performance, offers crypto-agility, and provides a simpler operational model.
Tessera is an evolution of Azure’s first integrated HSM model, incorporating insights gained from deploying Azure Integrated HSM at scale, and advances the technology through collaboration in the Open Compute Project, with the goal of broadly addressing the challenges of key and credential management in the era of AI and quantum computing.
Eliminating key management anti-patterns
In central HSM deployment models, HSM infrastructure is separate from compute resources, requiring cryptographic operations to traverse the network. The resulting latency and operational dependencies can lead enterprises to adopt workarounds that improve performance or availability but unintentionally weaken key protections. Some of these common key-management anti-patterns include:
- HSM keys may act as certificate authorities and endorse externally generated keys. These keys can then serve as trusted delegates without receiving the same hardware protection.
- HSM generated keys may be created as extractable and exported from the HSM in wrapped form. When used outside of the HSM the keys may not receive assurance levels equivalent to a FIPS 140-3 Level 3 HSM and become more susceptible to exfiltration or misuse.
Other anti-patterns include caching keys outside of HSMs for resilience, using software-held keys to reduce network latency to remote HSMs, sharing keys and security domains to simplify governance, and relying on proprietary protocols for interoperability. These practices intend to prioritize operational flexibility but can make key protection, policy enforcement, and auditable provenance less consistent across environments, undermining the security value HSMs are designed to provide.
The goal of Project Tessera is to advance the integrated HSM model to address these challenges in the industry, without compromising on security. The project will deliver Tessera Integrated HSM, a fully open-source integrated HSM designed to consistently enforce FIPS 140-3 Level 3 key protection throughout the key’s lifecycle.
By combining strong hardware-rooted protection with an open-source implementation and open protocols, Tessera Integrated HSM creates a path toward greater transparency, interoperability, and innovation across the HSM ecosystem. The native support for quantum-resilient cryptography will help ease the industry’s transition to post-quantum cryptography.
Demonstrating an open, interoperable HSM ecosystem
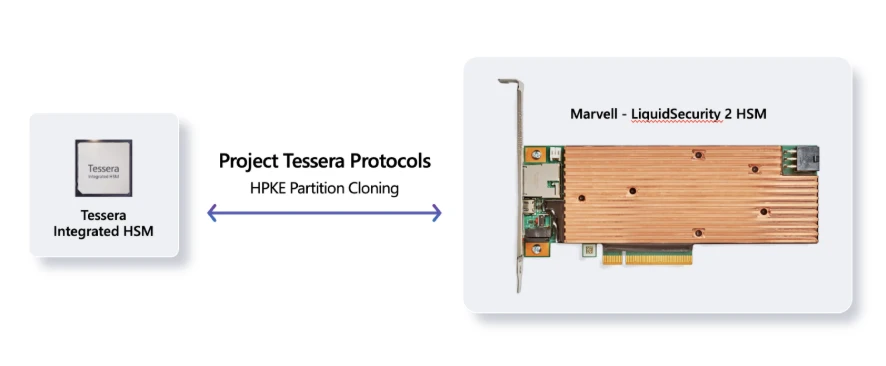
Today at the Open Compute Project Global Summit, Microsoft and Marvell® demonstrated the Tessera Integrated HSM transfer protocols establishing HSM partition cloning and resiliency rings across a Tessera Integrated HSM and a Marvell® LiquidSecurity® 2 HSM. The demonstration showed how two heterogeneous HSMs can operate in a resilient and unified security domain. Non-extractable keys within the security domain always remain protected within the HSMs and are available only to the authorized HSM partitions participating in the security domain and remain under the sole control of the partition owner.
The Tessera Integrated HSM protocols use post-quantum cryptography to protect communication between HSMs. This enables authorized workloads with a Tessera Integrated HSM to use both classical cryptography and post-quantum cryptographic services while their keys remain secured within the HSM boundary and can only be authorized for use by the key owner.
The Project Tessera specifications, protocols, software libraries, drivers, firmware, and hardware are available through the Tessera Integrated HSM GitHub. Going forward, this repository will add more open-source silicon, new hardware designs, and enhancements developed with the community.
Expanding Project Tessera through confidential computing
The early collaborators working on Project Tessera within the OCP community are exploring how the Tessera Integrated HSM key protection architecture can extend beyond systems with dedicated integrated HSM hardware. As part of this work, the project is making a minimal, unikernel-based Tessera firmware stack open source, designed to run within hardware-isolated confidential computing environments.
This implementation uses the same firmware stack as the hardware integrated HSM, extending a common security architecture across HSMs and confidential computing environments. In this model, cryptographic keys are protected within a confidential computing container, which provides cryptographic services to securely bound workloads, including worker containers and virtual machines. The initial implementation leverages AMD SEV-SNP and integrates with open-source virtualization technologies such as OpenVMM, with the Open Compute community working to extend support to other confidential computing architectures.
The complementary deployment models in Project Tessera extend strong key protection across systems with different hardware capabilities and assurance requirements. For platforms without dedicated integrated HSM hardware, confidential computing provides broadly deployable, hardware-isolated key protection with a minimal trusted computing base.
Project Tessera provides the highest level of hardware assurance, protecting keys within a dedicated, tamper-resistant security boundary designed to meet demanding certification requirements, including FIPS 140-3 Level 3 and Common Criteria.
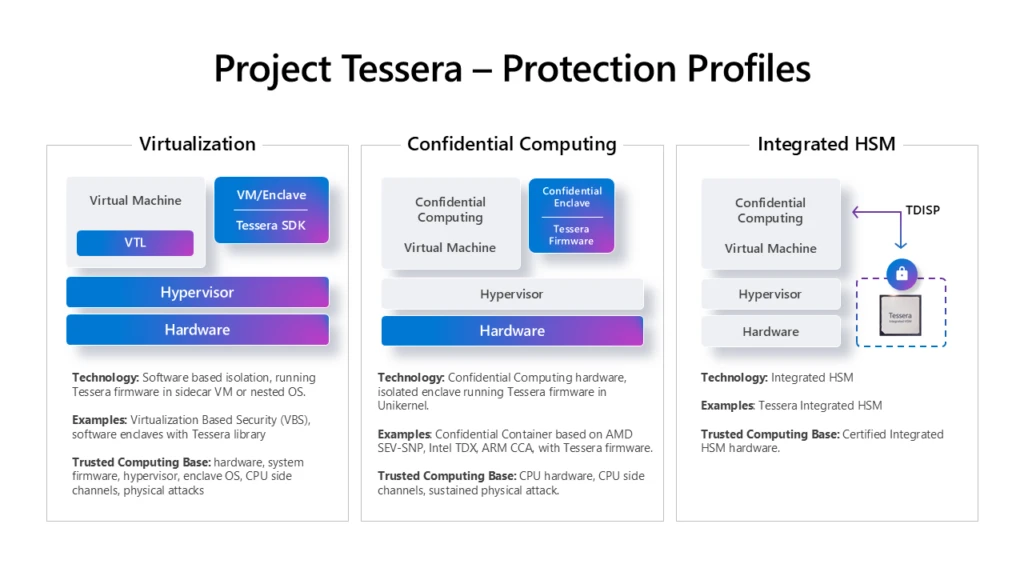
The deployment models share the same Project Tessera firmware and programming model, giving organizations a consistent foundation for cryptographic security across their infrastructure while providing a natural path to integrated HSM and higher levels of assurance in newer systems.
Together, these models make strong key protection accessible across a broad range of systems with different security assurance needs, all built on a common, open architecture. As the Open Compute Project community continues to advance Tessera Integrated HSM, we see an exciting opportunity for broader industry collaboration to strengthen key protection, expand secure key management, and accelerate innovation across the ecosystem.
For more information, visit the Microsoft booth at the Open Compute Project Global Summit for live demonstrations, explore Tessera Integrated HSM implementation on GitHub, and read the Microsoft Infrastructure Community blog for additional hardware security announcements: OCP2026 Hardware Security Updates.
Check out Microsoft’s presence at OCP Summit this year: aka.ms/OCP2026
Learn more about Azure Infrastructure: aka.ms/silicontosystems